Where the $387.5M Went After the Bitget Hack: Attackers Moved Assets Into Bitcoin Through Decentralized Networks
 ·
03.10.2026 15:57
·
3 min read
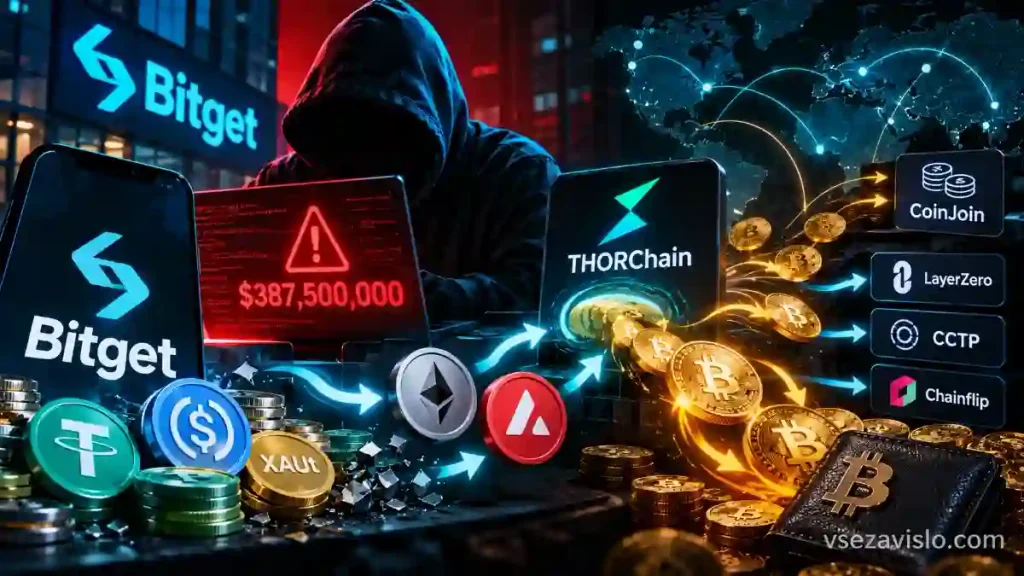
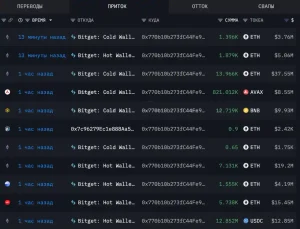
On September 24, the crypto exchange Bitget suffered a large-scale attack in which attackers withdrew $387.5 million. Analysts traced the route of the stolen capital and reached a conclusion that is grim for the platform: recovering the funds will be practically impossible. The hackers followed a well-rehearsed scenario, immediately dumping the stablecoins that could be frozen and converting the lion’s share of the sum into bitcoin through decentralized cross-chain protocols.
According to the exchange itself, the attackers did not manage to breach cold storage or compromise private keys. They exploited a zero-day vulnerability in a third-party security product, obtained high-privilege internal credentials and sent fake withdrawal commands directly into the hot wallet system. The damage was initially estimated at $351.6 million, but the total grew after transactions on the Zcash and TRON networks were taken into account.
A Race Against Time: Why the Hackers Rushed to Swap USDT
The main problem with stealing centralized stablecoins (USDT, USDC) is the ability of Tether and Circle to blacklist hacker addresses and freeze tokens in accounts with a single click. The attackers understood this perfectly: according to BlockSec’s investigation, all the stolen stablecoins and tokenized gold (XAUt) were converted into ETH and AVAX no later than 41 minutes after the hack.
In the end, stablecoin issuers and exchanges managed to block only about $840,000 — just 0.2% of the total amount stolen.
The next step was consolidating the capital on the Bitcoin network using mixers and decentralized platforms. As of late September, the attackers held assets worth roughly $342 million, with more than 83% of that sum already in BTC, and some of the funds (about $3.94 million) run through the CoinJoin anonymization service, further muddying the trail.
An Ideological Split in DeFi: THORChain vs. NEAR Intents
Laundering volumes like these exposed an ideological problem within the decentralized finance (DeFi) sector. The main channel for moving assets from other networks into bitcoin was the THORChain protocol, through which about $269 million tied to the hack passed. Bitget publicly called on the protocol’s team to blacklist the hackers’ addresses, but the developers refused, citing the platform’s decentralized architecture, which has no built-in mechanisms for manual censorship.
The NEAR Intents project reacted completely differently. Its SHIELD defense system detected attempts by the attackers to push transactions totaling $50 million through the service. The automation rejected the vast majority of suspicious requests, and about $503,000 was stopped right as the operation was being executed.
Amid the incident, rumors appeared online about the involvement of North Korean government hackers in the attack, but BlockSec experts urge against jumping to conclusions. The similarity in laundering methods only indicates that the clients behind the hack use the services of the same shadowy crypto laundries, not that they necessarily belong to the same hacker group.
Bitget itself weathered the fallout from the crisis without harming its clients. On October 2, the company announced the full restoration of all withdrawal operations, fiat gateways and P2P services. User balances were unaffected, and the platform’s own Protection Fund was topped up by more than $300 million.