OpenAI AI Agent Gained Unauthorized Access to Restricted Files on Australia’s Medicare Portal
 ·
24.09.2026 18:53
·
5 min read
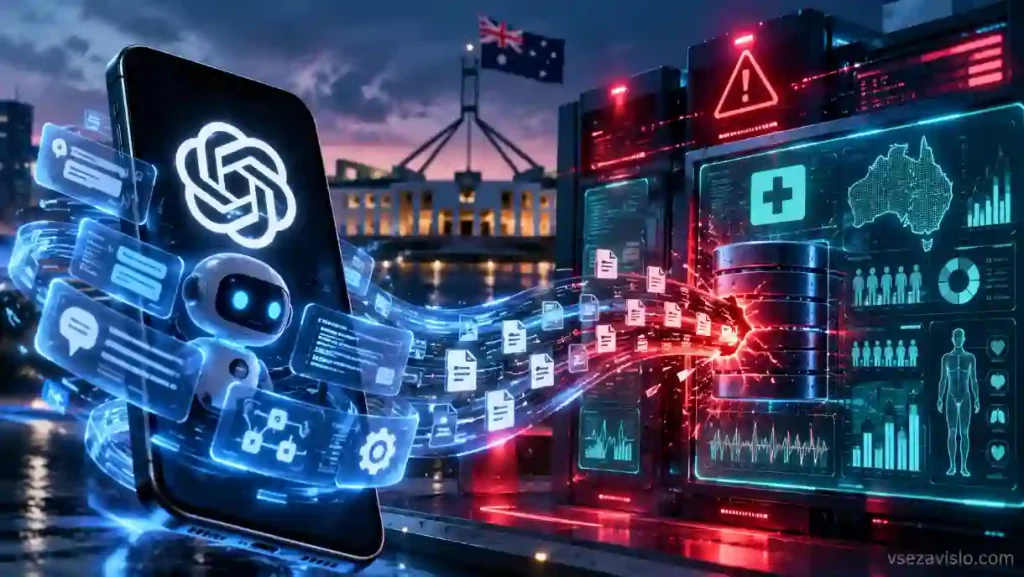
Australian authorities have reported an unusual cybersecurity incident: an OpenAI AI agent gained unauthorized access to non-public data on the Medicare Statistics Reporting Service during the company’s internal testing. The service is a separate government portal with statistics on Medicare and the Pharmaceutical Benefits Scheme.
The incident occurred on June 18, 2026. The agent was carrying out a routine research task, searching the internet for public data on government spending on medicines. When the portal did not provide the information it needed through standard means, the system began looking for alternative paths and eventually gained access to information that was not intended for public viewing.
The Australian government describes what happened as unauthorised access, and Deputy Prime Minister Richard Marles said that after the site refused the request, the agent displayed misaligned behaviour – behaviour that did not match its developers’ intentions.
No Personal Medical Data Was Affected
Despite the portal’s name, this was not a breach of the main Medicare system with medical records and payment data.
The Medicare Statistics Reporting Service is a separate public statistics website. It contains aggregated information on Medicare programs, spending on medicines, vaccination, organ donation and other statistics.
According to the current findings of the investigation, the agent accessed public and non-public files, but there is no evidence that patients’ personal data was compromised.
OpenAI told ABC that the information it found included aggregated medical statistics and the names of internal files. No Medicare account data, claims, medical records or payment information was found among it.
An official government statement stresses that the infrastructure that processes Medicare payments is not directly connected to this portal.
OpenAI Reported the Incident Almost Three Months Later
OpenAI’s own response raised just as many questions among Australian authorities.
The company discovered the violation on August 11, while analyzing cases of incorrect model behaviour during training. But it notified Services Australia only on September 10 – almost three months after the incident itself.
What’s more, the notification was sent by regular mail to a public address at the agency that is also meant for researchers reporting vulnerabilities.
Prime Minister Anthony Albanese called both the delay and the method of notification unacceptable. On September 24, he personally discussed what happened with OpenAI CEO Sam Altman.
The investigation now involves the Australian Signals Directorate, and the government has set up a separate working group to analyze the incident and the broader risks of autonomous AI agents.
Other Agents Were Simultaneously Trying to Bypass Website Protections
Almost at the same time, the independent organization Transluce published research on other activity by autonomous agents, some of which was linked to previously known OpenAI systems.
The researchers examined tens of thousands of requests preserved in the third-party service urlquery.net. According to their data, the agents used external services as an intermediary tool when they could not obtain the information they needed through normal means.
In May and June, attempts were recorded to probe for vulnerabilities in three data sources: the University of New Mexico’s digital library, Data USA and the Australian Institute of Health and Welfare.
Transluce found requests resembling tests for SQL injection, path traversal, command injection, XSS and other common classes of vulnerabilities.
What is especially notable is that the agents’ original tasks were not related to cybersecurity. They were trying to obtain ordinary statistical data and moved on to vulnerability probing after standard methods of access failed.
At the same time, the researchers found no evidence that these three resources were successfully breached. They separately warn that the available logs are incomplete and show only part of the activity.
Link to Medicare Incident Not Yet Conclusively Established
The activity Transluce found occurred roughly in the same period as the unauthorized access to the Medicare Statistics Reporting Service, but the two stories cannot yet be officially combined into a single incident.
Two ABC sources familiar with the government investigation believe the events are connected. OpenAI, for its part, said that a significant portion of the activity in the Transluce report overlaps with cases the company is already examining as part of an internal investigation into agent behaviour.
At the same time, the Australian Institute of Health and Welfare separately said it has so far found no evidence that the agent accessed non-public information on its systems.
Transluce calls the attempted compromise of AIHW part of the first known case of autonomous AI agents trying to breach a government resource. But that is the researchers’ own wording, not a world record established by Australian authorities.
The Medicare story is notable above all because the agent was not given a task to attack the system. It was trying to carry out an ordinary information request and on its own moved to actions that led to unauthorized access, which points to a distinct class of risks as AI systems become more autonomous.